Federated Learning & AI Privacy

Federated learning, differential privacy, and privacy-preserving machine learning. We cover how models train across devices and institutions without centralizing data, what privacy guarantees actually cost in accuracy, and the benchmarks and frameworks shaping the field, always traced back to the original research.

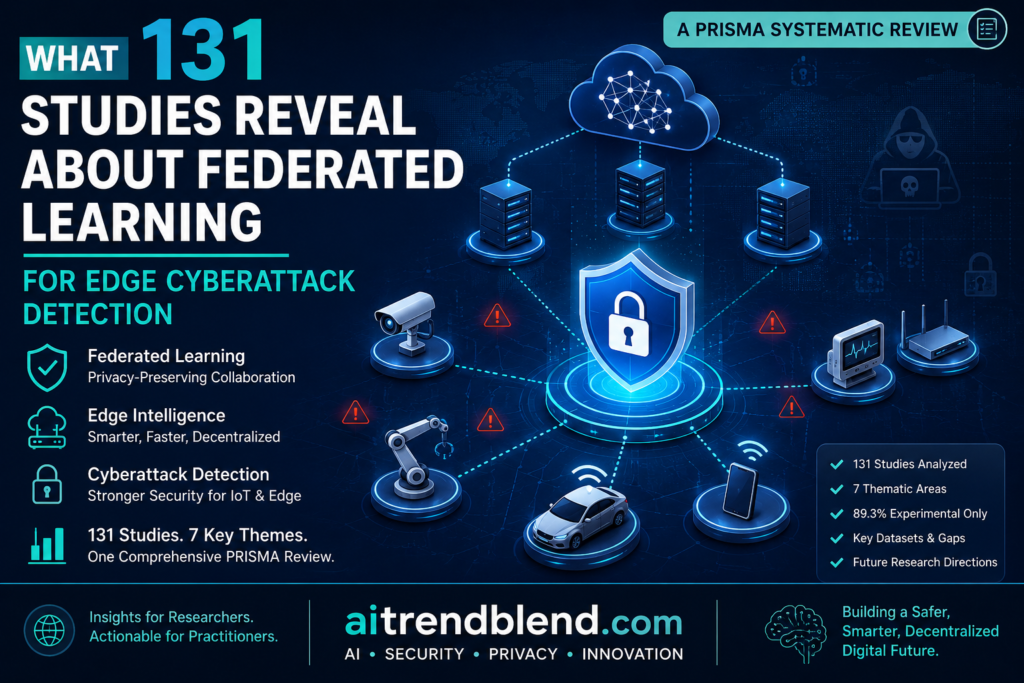
What 131 Studies Reveal About Federated Learning for Edge Cyberattack Detection

What 131 Studies Reveal About Federated Learning for Edge Cyberattack Detection

Edge computing exists because sending everything to the cloud is slow, expensive, and increasingly a privacy liability. Cameras, routers, industrial sensors, and vehicles now do a meaningful share of their own processing, which is great for latency and bandwidth. It…

What 131 Studies Reveal About Federated Learning for Edge Cyberattack Detection Read More »